In an increasingly interconnected world, the digital landscape for US businesses is constantly evolving, presenting both unprecedented opportunities and significant challenges. As we look towards 2026, the complexity and sophistication of cybersecurity threats are projected to reach new heights. Organizations that fail to adapt their defense mechanisms risk severe financial repercussions, reputational damage, and operational disruption. Understanding and preparing for these “Cybersecurity Threats 2026” is not just advisable; it’s imperative for survival and sustained growth.
This comprehensive guide will delve into the top five projected cybersecurity threats for US businesses in 2026, offering detailed insights into their nature and potential impact. More importantly, it will provide actionable, robust mitigation strategies to help your organization build a resilient cybersecurity posture against these formidable adversaries. From the pervasive menace of ransomware to the insidious risks lurking within artificial intelligence, we will explore how businesses can fortify their defenses and navigate the turbulent waters of the digital future.
The Evolving Landscape of Cybersecurity Threats 2026
The year 2026 promises a cybersecurity environment characterized by advanced persistent threats, nation-state-sponsored attacks, and the widespread exploitation of emerging technologies. Cybercriminals are no longer just opportunistic; they are highly organized, well-funded, and increasingly employing sophisticated tactics that blur the lines between traditional hacking and espionage. The proliferation of remote work, cloud computing, and the Internet of Things (IoT) has expanded the attack surface, making it harder for businesses to maintain a comprehensive security perimeter. Furthermore, the rapid advancements in artificial intelligence (AI) and machine learning (ML) are a double-edged sword: while they offer powerful tools for defense, they also empower attackers to create more potent and evasive threats. Businesses must recognize that “Cybersecurity Threats 2026” will demand a proactive, adaptive, and layered approach to security.
1. AI-Powered Attacks and Deepfakes: The New Frontier of Deception
Artificial intelligence, while a boon for many industries, is rapidly becoming a formidable weapon in the hands of cybercriminals. In 2026, expect a significant surge in AI-powered attacks, which leverage machine learning algorithms to automate and enhance malicious activities. These attacks can manifest in various forms, from highly sophisticated phishing campaigns that bypass traditional detection methods to autonomous malware that can learn and adapt to evade defenses. The true game-changer, however, will be the widespread use of deepfakes.
Deepfakes, AI-generated synthetic media that can convincingly imitate a person’s voice, face, or actions, pose an unprecedented threat to corporate security. Imagine a deepfake video of your CEO issuing fraudulent financial instructions, or an audio deepfake of a senior executive authorizing a suspicious wire transfer. These highly convincing deceptions can bypass even the most vigilant human scrutiny, leading to significant financial losses, reputational damage, and internal chaos. The ability of AI to generate realistic fake content at scale means that verifying the authenticity of digital communications will become a critical challenge for businesses.
Mitigation Strategies for AI-Powered Attacks and Deepfakes:
- Advanced AI-Driven Detection Systems: Implement AI/ML-based security solutions that can detect anomalies in network traffic, user behavior, and content, specifically trained to identify deepfake patterns and sophisticated phishing attempts.
- Robust Multi-Factor Authentication (MFA): Enforce MFA across all critical systems and accounts, especially for financial transactions and sensitive data access. This provides an additional layer of security even if credentials are compromised through deepfake social engineering.
- Employee Training and Awareness: Conduct regular, in-depth training sessions for employees on the dangers of deepfakes and AI-powered social engineering. Emphasize critical thinking, verification protocols for unusual requests, and the importance of reporting suspicious communications.
- Digital Forensics and Watermarking: Explore technologies for digital watermarking of official communications to prove authenticity. Develop incident response plans specifically for deepfake scenarios, including forensic tools to analyze potential synthetic media.
- Zero Trust Architecture: Adopt a Zero Trust security model, where no user or device is inherently trusted, regardless of their location. This requires strict verification for every access request, reducing the impact of compromised identities.
2. Highly Evasive Ransomware 2.0: Beyond Encryption
Ransomware has been a persistent and devastating threat for years, but in 2026, it will evolve into “Ransomware 2.0,” characterized by increased evasion techniques, double and triple extortion, and a focus on operational disruption rather than just data encryption. Attackers will leverage advanced obfuscation methods, polymorphic code, and fileless malware to bypass traditional endpoint detection and response (EDR) systems. The goal will be to remain undetected for longer periods, allowing them to gain deeper access and inflict maximum damage.
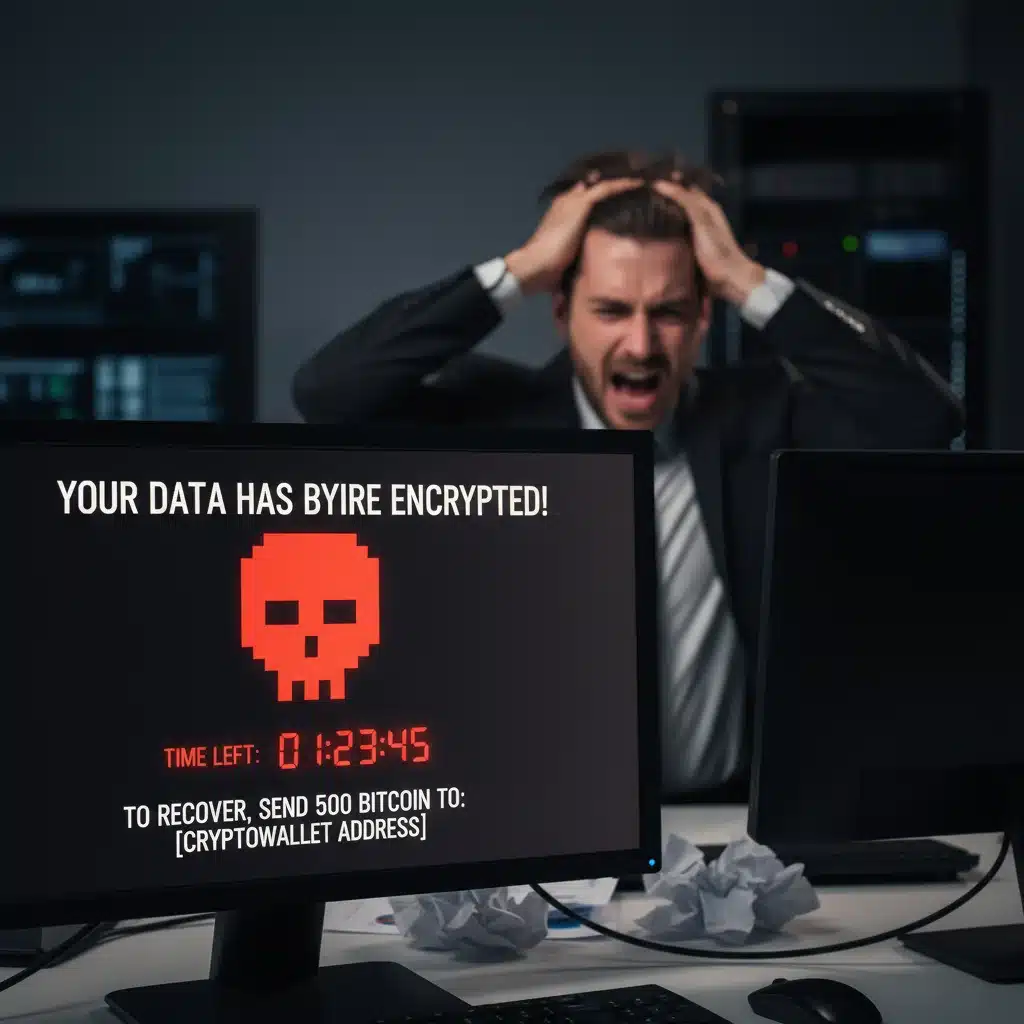
Beyond encrypting data, Ransomware 2.0 will intensify double extortion – exfiltrating sensitive data before encryption and threatening to publish it if the ransom isn’t paid. We will also see a rise in triple extortion, where attackers not only encrypt data and threaten to leak it, but also launch DDoS attacks against the victim’s infrastructure or directly contact their customers, partners, or even shareholders to pressure them into paying. The focus will shift from merely holding data hostage to crippling entire business operations, making recovery incredibly complex and costly.
Mitigation Strategies for Highly Evasive Ransomware 2.0:
- Advanced Endpoint Protection: Deploy next-generation antivirus (NGAV) and EDR solutions with behavioral analysis capabilities that can detect and prevent fileless and polymorphic ransomware.
- Immutable Backups and Disaster Recovery: Implement a robust backup strategy that includes immutable backups (data that cannot be altered or deleted) stored offsite and offline. Regularly test your disaster recovery plan to ensure swift restoration of operations.
- Network Segmentation and Microsegmentation: Segment your network to isolate critical systems and data. Microsegmentation can further limit the lateral movement of ransomware within your network, containing potential breaches.
- Proactive Threat Hunting: Implement threat hunting practices to actively search for hidden threats and vulnerabilities within your network before they can be exploited by ransomware.
- Privileged Access Management (PAM): Restrict and monitor privileged access to critical systems. Ransomware often exploits elevated privileges to spread rapidly and encrypt widespread data.
- Incident Response Plan for Ransomware: Develop a detailed incident response plan specifically for ransomware attacks, including communication protocols, legal counsel engagement, and negotiation strategies (though paying ransom is generally discouraged).
3. Supply Chain Attacks: Exploiting the Weakest Link
The interconnected nature of modern business means that an organization’s security is only as strong as its weakest link. In 2026, supply chain attacks are predicted to become even more prevalent and devastating. These attacks target an organization indirectly by compromising a less secure third-party vendor, software provider, or hardware manufacturer. Once a component in the supply chain is compromised, attackers can inject malicious code, backdoor software, or tamper with hardware, which then propagates to all downstream customers.
The impact of a single successful supply chain attack can be catastrophic, affecting hundreds or even thousands of businesses simultaneously, as seen with past incidents like SolarWinds. Attackers are increasingly focusing on software development pipelines, open-source components, and managed service providers (MSPs) as entry points. The challenge for US businesses is the sheer volume of third-party relationships and the difficulty in vetting the security posture of every partner.
Mitigation Strategies for Supply Chain Attacks:
- Vendor Risk Management (VRM) Programs: Establish a comprehensive VRM program to assess and continuously monitor the cybersecurity posture of all third-party vendors, suppliers, and partners. This includes security audits, contractual security requirements, and regular reviews.
- Software Bill of Materials (SBOM): Demand a Software Bill of Materials (SBOM) from all software vendors. An SBOM provides a complete list of all components, libraries, and dependencies used in a software product, allowing businesses to identify potential vulnerabilities.
- Secure Development Life Cycle (SDLC): Ensure that your software development processes and those of your critical vendors follow secure development best practices, including regular code reviews, vulnerability scanning, and penetration testing.
- Network Segmentation and Least Privilege: Isolate systems that interact with third-party components. Apply the principle of least privilege, ensuring that third-party access is restricted to only what is absolutely necessary.
- Continuous Monitoring of Third-Party Access: Implement tools and processes to continuously monitor and log all access by third-party vendors to your network and systems.
- Diversify Supply Chain: Where possible, diversify critical components and services across multiple vendors to reduce the impact of a single point of failure in the supply chain.
4. Identity-Based Attacks and Credential Theft: The Human Element
Despite technological advancements, the human element remains a primary target for cybercriminals. In 2026, identity-based attacks and credential theft will continue to be a dominant threat, evolving in sophistication. Phishing, spear-phishing, business email compromise (BEC), and social engineering tactics will leverage AI and deepfakes to become even more convincing and personalized. Attackers will focus on stealing credentials to gain initial access, then use them for lateral movement, privilege escalation, and data exfiltration.
The rise of “credential stuffing” – using lists of stolen usernames and passwords from breaches on other websites to gain access to accounts – will also intensify. Furthermore, the increasing reliance on single sign-on (SSO) and identity providers (IdPs) means that compromising one identity can grant access to a multitude of corporate resources. The challenge lies in protecting a distributed workforce, where employees access corporate resources from various devices and locations, making traditional perimeter security less effective.
Mitigation Strategies for Identity-Based Attacks and Credential Theft:
- Strong Authentication Practices: Mandate robust multi-factor authentication (MFA) for all users and systems, especially for accessing sensitive data and applications. Consider passwordless authentication solutions where feasible.
- Identity and Access Management (IAM) Systems: Implement comprehensive IAM solutions to manage user identities, control access to resources, and enforce least privilege principles. Regularly review and revoke unnecessary access.
- Security Awareness Training: Provide continuous and updated security awareness training to employees, focusing on recognizing sophisticated phishing, spear-phishing, BEC, and social engineering attempts. Conduct simulated phishing exercises regularly.
- Endpoint Detection and Response (EDR): Deploy EDR solutions that can detect suspicious activities on endpoints, such as credential dumping, lateral movement, and unauthorized access attempts.
- Principle of Least Privilege: Ensure that users and applications only have the minimum necessary access rights to perform their functions. Regularly audit and adjust permissions.
- Monitoring User Behavior Analytics (UBA): Utilize UBA tools to detect anomalous user behavior that could indicate a compromised account or insider threat.
5. Critical Infrastructure Targeting and OT/IoT Exploitation
As industries increasingly adopt digital transformation, the convergence of Information Technology (IT) and Operational Technology (OT) networks, along with the proliferation of IoT devices, creates new vulnerabilities. In 2026, critical infrastructure – including energy grids, water treatment plants, transportation systems, and healthcare facilities – will face an elevated threat of cyberattacks. These attacks aim not just for data theft, but for physical disruption, sabotage, and even loss of life.
OT systems, often designed for reliability and longevity rather than security, are becoming increasingly connected to the internet, making them accessible to remote attackers. IoT devices, from smart sensors in manufacturing plants to medical devices in hospitals, are often deployed with weak security defaults, unpatched vulnerabilities, and limited update capabilities, making them easy targets. Exploiting these vulnerabilities can lead to severe consequences, including power outages, environmental damage, and compromised public safety. The “Cybersecurity Threats 2026” in this domain require specialized expertise and a deep understanding of industrial control systems.
Mitigation Strategies for Critical Infrastructure Targeting and OT/IoT Exploitation:
- IT/OT Convergence Security: Implement security solutions specifically designed for IT/OT convergence, providing visibility, monitoring, and control across both environments.
- Network Segmentation for OT/IoT: Strictly segment OT and IoT networks from IT networks. Use firewalls and intrusion detection/prevention systems (IDS/IPS) to control traffic flow between segments.
- Vulnerability Management for OT/IoT: Conduct regular vulnerability assessments and penetration testing on OT systems and IoT devices. Develop a patching strategy that considers the unique operational constraints of these environments.
- Secure by Design: When deploying new IoT devices or OT systems, prioritize those designed with security in mind, including secure boot, encrypted communications, and robust authentication.
- Anomaly Detection and Behavioral Monitoring: Implement systems that monitor OT and IoT networks for unusual activity or deviations from normal operating parameters, which could indicate a cyberattack.
- Physical Security and Access Control: Enhance physical security measures for critical infrastructure components and OT devices, as physical access can often bypass digital controls.
- Incident Response Plans for OT/IoT: Develop specific incident response plans for OT/IoT environments, addressing the unique challenges of responding to attacks that could impact physical processes.
Building a Resilient Cybersecurity Posture for 2026
Successfully navigating the “Cybersecurity Threats 2026” requires more than just reactive measures; it demands a proactive, holistic, and adaptive security strategy. US businesses must shift from a perimeter-focused defense to a comprehensive, multi-layered approach that integrates technology, processes, and people.
Key Pillars of a Robust Cybersecurity Strategy:
- Continuous Risk Assessment: Regularly assess your organization’s risk posture, identifying critical assets, potential vulnerabilities, and the likelihood and impact of various threats. Use this assessment to prioritize security investments.
- Security by Design: Integrate security considerations into every stage of your business processes, from software development to infrastructure deployment. It’s far more effective and cost-efficient to build security in from the start than to bolt it on later.
- Proactive Threat Intelligence: Stay informed about the latest “Cybersecurity Threats 2026” and emerging attack vectors. Subscribe to threat intelligence feeds, participate in industry information sharing groups, and leverage security experts.
- Automated Security Solutions: Utilize automation in security operations to enhance detection, response, and remediation capabilities. Security orchestration, automation, and response (SOAR) platforms can significantly improve efficiency.
- Strong Governance, Risk, and Compliance (GRC): Establish clear cybersecurity policies, procedures, and governance frameworks. Ensure compliance with relevant industry regulations and data privacy laws (e.g., CCPA, HIPAA, GDPR).
- Regular Audits and Penetration Testing: Conduct independent security audits and penetration tests regularly to identify weaknesses in your defenses and validate the effectiveness of your security controls.
- Cybersecurity Insurance: While not a mitigation strategy in itself, robust cybersecurity insurance can help mitigate the financial impact of a successful cyberattack, covering costs related to incident response, legal fees, and business interruption.
- Culture of Security: Foster a strong security culture within your organization, where every employee understands their role in protecting digital assets. Regular training, clear communication, and leadership buy-in are crucial.
The Future is Now: Preparing for What’s Next
The landscape of “Cybersecurity Threats 2026” is complex and ever-changing, but with informed strategies and diligent execution, US businesses can significantly enhance their resilience. The key is to move beyond simply reacting to threats and instead adopt a proactive, adaptive, and predictive security posture. By investing in advanced technologies, fostering a security-aware workforce, and implementing robust governance, organizations can transform cybersecurity from a mere cost center into a strategic business enabler.
Remember, cybersecurity is not a one-time project but an ongoing journey. Continuous improvement, regular assessments, and staying abreast of the latest threat intelligence are vital. The businesses that thrive in 2026 and beyond will be those that embrace cybersecurity as a core component of their operational strategy, safeguarding their data, their customers, and their future.