Cybersecurity 2026: Quantum Threats to US Critical Infrastructure – A 6-Step Guide
Cybersecurity 2026: Protecting US Critical Infrastructure from Quantum Computing Threats – A 6-Step Guide
The year 2026 is closer than it appears on the calendar, and with it comes an increasingly urgent and complex challenge for national security and economic stability: the looming threat of quantum computing to US critical infrastructure. While quantum computers promise revolutionary advancements, their immense computational power also presents an existential risk to current cryptographic standards. This paradigm shift could render today’s most robust encryption obsolete, leaving vital systems – from energy grids and financial networks to communication systems and defense infrastructure – vulnerable to unprecedented attacks. This article delves into the critical implications of this technological evolution and provides a comprehensive, 6-step guide for safeguarding US critical infrastructure in the face of emerging quantum cybersecurity threats.
The stakes couldn’t be higher. A successful quantum attack on critical infrastructure could lead to widespread disruption, economic collapse, and even loss of life. Understanding and mitigating these risks through proactive measures is not merely advisable but an absolute imperative. Our focus here is on actionable strategies, designed to equip policymakers, cybersecurity professionals, and infrastructure operators with the knowledge and tools needed to navigate this complex landscape. We will explore the nature of the quantum threat, its specific impact on critical infrastructure, and outline a strategic roadmap to build resilient, quantum-resistant defenses by 2026.
Understanding the Quantum Threat to US Critical Infrastructure
To effectively address the challenge, we must first grasp the fundamental nature of the quantum threat. Quantum computers leverage the principles of quantum mechanics – superposition, entanglement, and interference – to perform calculations far beyond the capabilities of even the most powerful classical supercomputers. While general-purpose, fault-tolerant quantum computers are still some years away, the rapid pace of development suggests that cryptographically relevant quantum computers (CRQCs) could emerge within the next decade, with some estimates putting them as early as 2026. This timeline aligns precisely with the need for immediate action.
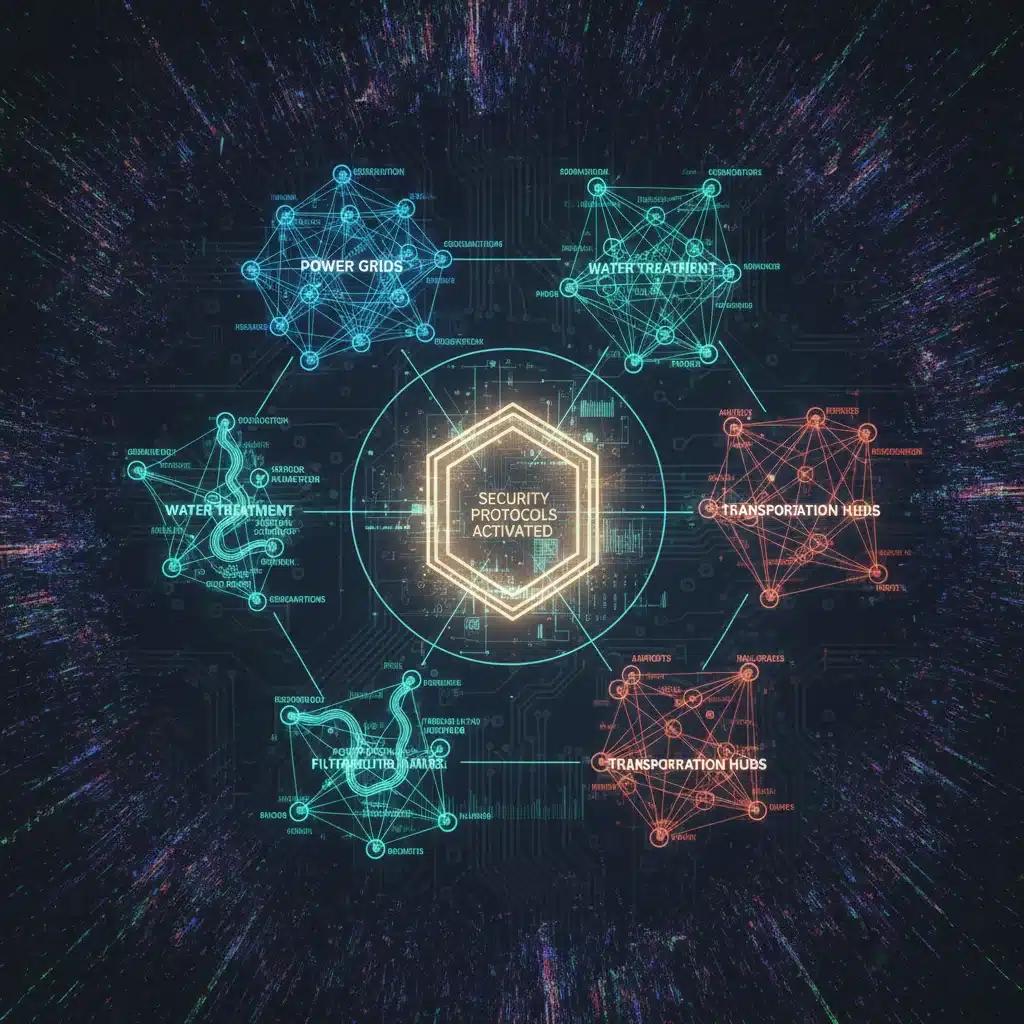
The primary concern for US critical infrastructure lies in the ability of quantum algorithms, particularly Shor’s algorithm, to break widely used public-key cryptographic schemes such as RSA and Elliptic Curve Cryptography (ECC). These algorithms form the bedrock of digital security, protecting everything from secure communications (HTTPS, VPNs) and digital signatures to data encryption at rest and in transit. Once these systems are compromised, adversaries could decrypt sensitive data, forge digital identities, and gain unauthorized access to critical operational technology (OT) and industrial control systems (ICS) that manage infrastructure.
Furthermore, Grover’s algorithm poses a threat to symmetric-key cryptography (e.g., AES) and hash functions, though its impact is less severe than Shor’s. While it doesn’t break these algorithms entirely, it significantly reduces their effective key length, necessitating a doubling of key sizes to maintain equivalent security levels. The cumulative effect of these quantum capabilities creates a ticking time bomb for any system relying on current cryptographic primitives, especially those with long data retention requirements or systems that are difficult to update, such as legacy infrastructure.
The "harvest now, decrypt later" threat is also a significant concern. Malicious actors could be collecting encrypted sensitive data today, anticipating that they will be able to decrypt it once powerful quantum computers become available. This means that even data encrypted today, if intercepted, could be compromised in the future, posing a long-term risk to national security and proprietary information.
Step 1: Conduct a Comprehensive Quantum-Readiness Assessment
The first and most crucial step in protecting US critical infrastructure is to understand the current cryptographic landscape within each organization. This requires a detailed and thorough quantum-readiness assessment. This isn’t just an IT audit; it’s a deep dive into every system, application, and data flow that relies on cryptography.
Begin by identifying all cryptographic assets. This includes all public-key infrastructure (PKI) elements, digital certificates, encryption protocols used for data at rest and in transit, authentication mechanisms, and secure communication channels. Catalog every instance where RSA, ECC, or other potentially vulnerable algorithms are employed. This task is often more complex than it sounds, given the distributed and often opaque nature of critical infrastructure systems, which can span decades of technological evolution and multiple vendors.
Next, assess the "cryptographic agility" of your systems. How easily can cryptographic algorithms and key sizes be updated or replaced? Many legacy systems within critical infrastructure were not designed with cryptographic agility in mind, making updates challenging, costly, or even impossible without significant downtime. Identify these "crypto-agile" and "crypto-fragile" components.
Simultaneously, evaluate the "data lifetime" and "threat lifetime" for all sensitive data. How long does the data need to remain confidential? How long could an adversary conceivably store intercepted encrypted data before a quantum computer becomes available to decrypt it? This analysis will help prioritize mitigation efforts, focusing on data with long confidentiality requirements that are currently protected by vulnerable cryptography. For example, classified government communications or proprietary industrial designs might require protection for decades, making them prime targets for future quantum decryption.
Finally, identify all third-party dependencies. Critical infrastructure relies heavily on a complex supply chain of vendors, software providers, and service providers. Their cryptographic posture directly impacts your own. Engage with these partners to understand their quantum readiness plans and ensure their solutions will be compatible with post-quantum standards.
Step 2: Develop a Strategic Post-Quantum Cryptography (PQC) Migration Roadmap
Once the assessment is complete, the next step is to formulate a clear, actionable PQC migration roadmap. This roadmap should be a multi-year plan, acknowledging that a complete transition cannot happen overnight. It needs to be integrated into broader cybersecurity strategies and budget cycles, ensuring adequate resources are allocated.
The National Institute of Standards and Technology (NIST) is at the forefront of standardizing quantum-resistant algorithms. As of 2022, NIST announced the first set of quantum-resistant algorithms, with more expected in the coming years. The migration roadmap must closely follow NIST’s recommendations, prioritizing the implementation of these new standards as they become stable and widely adopted.
The roadmap should outline a phased approach. Initial phases might focus on "hybrid mode" cryptography, where both classical and post-quantum algorithms are used in parallel. This provides a layer of security even if one of the algorithms is compromised, offering a fallback while the new standards mature and gain wider acceptance. This dual-layer approach is a prudent interim measure to maintain robust security during the transition.
Prioritization is key. Systems and data identified as most vulnerable and critical in the quantum-readiness assessment should be addressed first. This includes systems handling highly sensitive data, long-lived data, and those with significant national security implications. Also, consider the cost and complexity of migration for different systems. Some legacy systems might require complete overhauls, while others might be updated with software patches.
The roadmap should also include provisions for testing and validation. Migrating to new cryptographic primitives is a complex undertaking, and thorough testing is essential to ensure that the new algorithms are correctly implemented, perform as expected, and do not introduce new vulnerabilities or operational disruptions. Collaboration with vendors and external experts will be crucial here.
Step 3: Invest in Quantum-Resistant Technologies and Skills
The transition to quantum-resistant cryptography requires significant investment, not only in new technologies but also in human capital. Organizations responsible for US critical infrastructure must allocate budgets for research, development, and procurement of PQC solutions.
This includes investing in cryptographic modules, hardware security modules (HSMs) that support new algorithms, and software libraries that integrate NIST-approved PQC. Furthermore, consider the emerging field of quantum key distribution (QKD) as a potential complementary technology, although QKD has its own limitations regarding distance and infrastructure requirements. While not a direct replacement for PQC, QKD can offer a highly secure method for exchanging cryptographic keys in specific scenarios.
Equally important is the investment in skills development. The current cybersecurity workforce often lacks expertise in quantum computing and post-quantum cryptography. Training programs must be established to upskill existing personnel and attract new talent with specialized knowledge in these areas. This includes understanding the mathematical underpinnings of PQC, implementation best practices, and the operational challenges of deploying new cryptographic systems. Partnerships with academic institutions and specialized training providers can help bridge this knowledge gap.
Moreover, foster a culture of continuous learning and adaptation. The field of quantum computing is evolving rapidly, and what is considered secure today might be vulnerable tomorrow. Regular updates to knowledge, tools, and strategies will be essential to maintain a robust defense against quantum cybersecurity threats.
Step 4: Enhance Supply Chain Security and Collaboration
Critical infrastructure is inherently interconnected, relying on a vast and complex supply chain. The security of this chain is only as strong as its weakest link. A quantum vulnerability introduced by a single vendor could compromise an entire system. Therefore, enhancing supply chain security is paramount in the context of quantum cybersecurity.
Organizations must establish rigorous vendor management programs that specifically address quantum readiness. This includes requiring vendors to provide roadmaps for PQC migration in their products and services, incorporating PQC requirements into contracts, and conducting regular audits of their cryptographic practices. Prioritize vendors who are actively engaged with NIST PQC standardization efforts and demonstrate a clear commitment to quantum-resistant solutions.
Beyond individual vendor relationships, fostering broader collaboration across the critical infrastructure sectors and with government agencies is vital. Information sharing about emerging quantum threats, successful migration strategies, and lessons learned will accelerate the collective defense posture. Government initiatives, such as those led by CISA (Cybersecurity and Infrastructure Security Agency) and NIST, play a crucial role in coordinating these efforts, providing guidance, and facilitating the development of common standards and best practices.
Consider establishing sector-specific working groups focused on quantum cybersecurity. These groups can share threat intelligence, develop common architectural patterns for PQC deployment, and advocate for policy changes that support a coordinated national response. This collaborative approach ensures that no single entity is left to tackle the quantum challenge in isolation, strengthening the overall resilience of US critical infrastructure against quantum cybersecurity threats.
Step 5: Implement Robust Cryptographic Key Management Practices
The transition to post-quantum cryptography will involve managing an entirely new set of cryptographic keys, potentially larger and more complex than current ones. Robust key management practices are essential to prevent the compromise of these new quantum-resistant keys, which could undermine the entire PQC migration effort. This represents a critical component of any comprehensive quantum cybersecurity strategy.
Review and update existing key management policies and procedures. This includes key generation, distribution, storage, rotation, revocation, and destruction. Ensure that all key management systems (KMS) are capable of handling the new PQC algorithms and key sizes. Consider the use of hardware security modules (HSMs) for storing and managing critical keys, as they provide a higher level of physical and logical protection.
Particular attention should be paid to the lifecycle management of PQC keys. Given the potential for future advancements in quantum computing, keys might need to be rotated more frequently than currently practiced. Automating key management processes where possible can reduce human error and improve efficiency. Implement strong access controls and audit trails for all key management operations to detect and prevent unauthorized access or manipulation.
Furthermore, consider the implications of quantum random number generators (QRNGs) for key generation. While classical pseudo-random number generators are generally considered secure, QRNGs offer a truly random source, which can enhance the strength of cryptographic keys. Integrating QRNGs into key generation processes could provide an additional layer of security against future, unforeseen quantum attacks that might exploit weaknesses in classical randomness.
Step 6: Develop and Practice Quantum Incident Response Plans
Even with the most meticulous planning and implementation, the possibility of a quantum-related security incident cannot be entirely eliminated. Therefore, developing and regularly practicing quantum incident response plans is a non-negotiable component of a robust quantum cybersecurity strategy for US critical infrastructure.
These plans should be an extension of existing cybersecurity incident response frameworks but tailored to the unique challenges posed by quantum threats. This includes defining clear roles and responsibilities, communication protocols, and escalation procedures specifically for quantum-related compromises. For instance, how would an organization respond if it discovered that its encrypted data had been compromised by a quantum computer, or if a critical system’s digital signature was forged using a quantum algorithm?
The incident response plan should cover various scenarios, such as the discovery of a vulnerability in a PQC algorithm, the compromise of PQC keys, or evidence of a "harvest now, decrypt later" attack. It should also outline procedures for forensic analysis in a quantum context, data recovery, and mitigation strategies to minimize the impact of a breach.
Regular tabletop exercises and simulations are crucial for testing the effectiveness of these plans. These exercises should involve not only internal cybersecurity teams but also relevant stakeholders from operational technology, legal, communications, and executive leadership. Practicing these scenarios will help identify weaknesses in the plan, improve coordination, and ensure a rapid and effective response when a real incident occurs. The goal is to build resilience, ensuring that even in the face of a successful quantum attack, critical infrastructure can recover quickly and maintain essential services.
The Path Forward: Securing US Critical Infrastructure Beyond 2026
The challenge of quantum cybersecurity for US critical infrastructure is immense, but not insurmountable. By taking proactive steps today, guided by the 6-step framework outlined above, organizations can significantly bolster their defenses against the quantum threat. The timeline to 2026 is tight, emphasizing the urgency of these actions. Delay is not an option when the foundational security of national infrastructure is at stake.
This journey will require continuous vigilance, adaptability, and collaboration across government, industry, and academia. The landscape of quantum computing and cryptography is dynamic, demanding ongoing research, development, and refinement of security strategies. Investing in quantum cybersecurity infrastructure is not just a technological upgrade; it is an investment in national security, economic stability, and the continued functioning of society.
By embracing these strategies – conducting thorough assessments, developing clear migration roadmaps, investing in new technologies and skills, strengthening supply chains, implementing robust key management, and practicing incident response – the US can ensure that its critical infrastructure remains resilient and secure in the quantum era. The future of quantum cybersecurity infrastructure depends on the decisive actions taken today.