Navigating Data Privacy Concerns: 4 Strategies to Build Consumer Confidence in 2026
In the rapidly evolving digital landscape of 2026, data has become the new currency. Businesses across all sectors rely on vast amounts of consumer data to personalize experiences, optimize services, and drive innovation. However, with this increasing reliance comes an equally significant challenge: data privacy concerns. Consumers are more aware than ever of the value of their personal information and the potential risks associated with its collection and use. High-profile data breaches, regulatory shifts, and a growing demand for transparency have created an environment where consumer trust is fragile and hard-won. For any organization aiming to thrive in this new era, navigating these concerns and proactively building consumer confidence through robust Data Privacy Strategies is not just good practice; it’s an absolute necessity.
The stakes are incredibly high. A single data breach can not only result in severe financial penalties and legal repercussions but can also irrevocably damage a brand’s reputation, leading to a significant loss of customer loyalty and market share. Conversely, organizations that prioritize and visibly demonstrate their commitment to data privacy can differentiate themselves, fostering deeper trust and stronger relationships with their customer base. This article will delve into four critical Data Privacy Strategies that businesses must implement and refine by 2026 to effectively address data privacy concerns and cultivate a steadfast sense of consumer confidence.
From enhancing transparency and bolstering cybersecurity measures to embracing ethical AI and ensuring global regulatory compliance, these strategies form a comprehensive framework for safeguarding personal data and empowering consumers. By proactively adopting these approaches, businesses can move beyond mere compliance to become true stewards of customer information, transforming data privacy from a regulatory burden into a powerful competitive advantage.
Strategy 1: Radical Transparency and Clear Communication
One of the most potent tools in building consumer confidence regarding data privacy is radical transparency. In an age where data collection practices can often feel opaque and confusing, consumers crave clarity. They want to understand what data is being collected, why it’s being collected, how it’s being used, and who has access to it. This goes beyond merely having a privacy policy buried deep within a website; it requires a proactive and accessible approach to communication.
Simplifying Privacy Policies
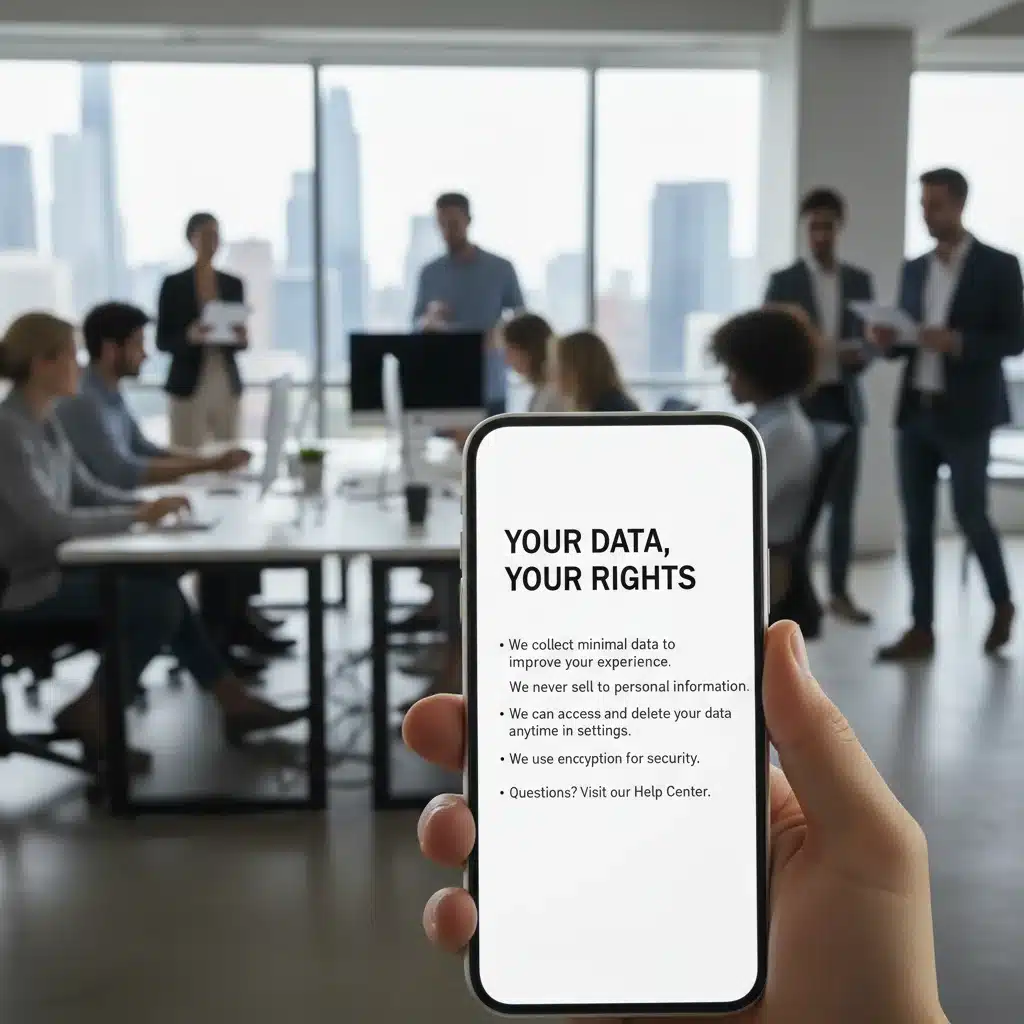
Traditionally, privacy policies have been lengthy, jargon-filled legal documents that few consumers actually read or comprehend. By 2026, businesses must transform these documents into easily digestible, user-friendly resources. This means:
- Plain Language: Ditching legalistic terminology for clear, concise language that the average person can understand.
- Layered Approach: Offering a summary or a dashboard view of key privacy settings and data usage, with options to delve into more detailed information if desired. Think of it like nutritional labels for data.
- Visual Aids: Utilizing infographics, videos, and interactive tools to explain complex data flows and privacy choices.
- Accessibility: Ensuring privacy information is readily available on all platforms, including mobile apps, and is accessible to individuals with disabilities.
Google, for instance, has made strides in this area by providing users with a “Privacy Checkup” tool that allows them to review and adjust their privacy settings in a step-by-step, intuitive manner. This empowers users and fosters a sense of control over their data.
Proactive Data Usage Disclosure
Transparency should extend to every interaction where data is collected. This involves:
- Just-in-Time Notifications: Informing users about data collection at the point of interaction. For example, a pop-up explaining why an app needs access to location data when that feature is first used.
- Clear Opt-in/Opt-out Mechanisms: Making it unequivocally simple for users to consent to or decline specific data collection and processing activities. Granular controls, rather than all-or-nothing options, are crucial.
- Regular Updates: Communicating any significant changes to data practices or privacy policies well in advance and explaining the implications clearly.
- Data Minimization Explanations: Articulating how the organization adheres to the principle of data minimization, only collecting the data absolutely necessary for a given purpose. This reassures consumers that their data isn’t being hoarded unnecessarily.
Companies like Apple have set a high bar with their App Tracking Transparency (ATT) feature, which requires apps to ask for user permission before tracking their activity across other companies’ apps and websites. This puts the power directly in the user’s hands and has significantly influenced consumer expectations regarding data control.
Building a Culture of Transparency
True transparency isn’t just about external communication; it’s about embedding a culture of data ethics and transparency within the organization itself. This means:
- Employee Training: Ensuring all employees, especially those involved in data handling, understand the company’s privacy policies and the importance of data protection.
- Privacy by Design: Integrating privacy considerations into the design and development of all products, services, and systems from the outset, rather than as an afterthought.
- Accountability: Establishing clear internal processes for handling data subject access requests, privacy complaints, and data breach responses, and communicating these processes to consumers where appropriate.
By making transparency a core organizational value, businesses can build a foundation of trust that resonates with consumers and positions them as responsible data stewards. This proactive approach to communication is a cornerstone of effective Data Privacy Strategies.
Strategy 2: Robust Cybersecurity and Data Protection
Transparency is vital, but it must be coupled with an ironclad commitment to securing the data that consumers entrust to businesses. In 2026, the sophistication of cyber threats continues to escalate, making robust cybersecurity measures more critical than ever. A single breach can undermine years of trust-building efforts. Therefore, implementing advanced data protection mechanisms is a non-negotiable component of any effective set of Data Privacy Strategies.
Implementing Advanced Encryption and Anonymization
Protecting data at rest and in transit is fundamental. This involves:
- End-to-End Encryption: Ensuring that data is encrypted from the point of collection to its storage and processing. This makes it unreadable to unauthorized parties, even if intercepted.
- Homomorphic Encryption: Exploring and implementing advanced encryption techniques that allow computations to be performed on encrypted data without decrypting it first, further enhancing privacy. While still emerging, its applications are growing.
- Pseudonymization and Anonymization: Where possible, converting identifiable data into a pseudonymized or anonymized format. Pseudonymization replaces direct identifiers with artificial ones, while anonymization removes all identifying information, making it impossible to link data back to an individual. This is particularly useful for analytics and research.
- Secure Multi-Party Computation (SMC): Utilizing techniques that allow multiple parties to jointly compute a function over their inputs while keeping those inputs private.
Leading cloud providers are continuously enhancing their encryption offerings, often making them default for data stored on their platforms. Businesses leveraging these services must ensure they are utilizing the highest available security standards and configuration options.
Proactive Threat Detection and Incident Response
The best defense is often a good offense. This means having systems in place to detect and respond to threats before they escalate:
- AI-Powered Threat Detection: Employing artificial intelligence and machine learning to analyze network traffic, user behavior, and system logs for anomalies that indicate potential cyber threats. AI can identify patterns that human analysts might miss, offering real-time insights into emerging attacks.
- Regular Security Audits and Penetration Testing: Continuously testing systems for vulnerabilities through independent audits and simulated cyberattacks. This helps identify weaknesses before malicious actors exploit them.
- Automated Incident Response: Developing and automating incident response plans to quickly contain breaches, minimize damage, and restore systems. This includes clear communication protocols for informing affected individuals and regulatory bodies.
- Zero-Trust Architecture: Adopting a zero-trust security model, which assumes no user or device, whether inside or outside the network, should be trusted by default. Every access attempt must be verified, significantly reducing the attack surface.
Companies like Microsoft and IBM are at the forefront of developing AI-driven cybersecurity solutions that can detect and neutralize threats with unprecedented speed and accuracy. Integrating such technologies is becoming essential.
Employee Training and Awareness
Human error remains one of the largest vectors for data breaches. Therefore, comprehensive and ongoing employee training is indispensable:
- Regular Cybersecurity Training: Conducting mandatory, regular training sessions on phishing awareness, password hygiene, social engineering tactics, and secure data handling practices.
- Simulated Phishing Attacks: Periodically conducting simulated phishing campaigns to test employee vigilance and reinforce training.
- Secure Development Practices: Training developers on secure coding practices to prevent vulnerabilities from being built into software from the ground up.
- Clear Policies and Procedures: Ensuring employees are aware of and adhere to strict data security policies, including those related to remote work, device security, and data sharing.
By investing in both advanced technological defenses and human-centric security education, businesses can create a multi-layered defense system that significantly reduces the risk of data breaches, thereby solidifying consumer trust in their Data Privacy Strategies.
Strategy 3: Ethical AI and Data Governance
As artificial intelligence becomes increasingly integrated into business operations, from personalized recommendations to automated decision-making, the ethical implications of how AI uses personal data come to the forefront. By 2026, consumers will expect not only secure data handling but also ethical data processing, particularly when AI is involved. This necessitates a strong focus on ethical AI principles and robust data governance frameworks as integral parts of any comprehensive set of Data Privacy Strategies.
Developing and Deploying Ethical AI Principles
The power of AI to analyze vast datasets and make predictions or decisions requires a conscious commitment to ethical guidelines:
- Fairness and Bias Mitigation: Actively working to identify and mitigate biases in AI models and the data they are trained on. Biased AI can lead to discriminatory outcomes, eroding trust and potentially violating anti-discrimination laws. Regular audits of AI systems for fairness are crucial.
- Transparency and Explainability (XAI): Striving for explainable AI where possible. Consumers and regulators should be able to understand how an AI system arrived at a particular decision, especially if that decision significantly impacts an individual (e.g., credit scores, loan approvals).
- Accountability: Establishing clear lines of responsibility for AI systems and their outcomes. Who is accountable when an AI makes an error or causes harm due to data misuse?
- Human Oversight: Ensuring that AI systems are not fully autonomous, especially in critical decision-making processes. Human oversight and intervention capabilities must always be maintained.
- Privacy-Preserving AI: Exploring and implementing techniques like federated learning and differential privacy, which allow AI models to be trained on decentralized datasets without directly exposing individual user data.
Organizations like Google and IBM have published their own ethical AI guidelines, demonstrating a growing recognition within the tech industry of the need for responsible AI development. Businesses must follow suit and tailor these principles to their specific contexts.
Establishing Robust Data Governance Frameworks
Effective data governance provides the structure and processes necessary to manage data as a strategic asset, ensuring its quality, security, and ethical use throughout its lifecycle. This is particularly vital for AI applications:
- Data Quality Management: Implementing processes to ensure the accuracy, completeness, and consistency of data. Poor data quality can lead to flawed AI insights and unfair outcomes.
- Data Lifecycle Management: Defining policies for data collection, storage, retention, archiving, and destruction. This ensures data is only kept for as long as necessary and is securely disposed of when no longer needed.
- Role-Based Access Control: Implementing strict controls over who can access, modify, and use specific datasets, especially sensitive personal information. This minimizes the risk of internal data misuse.
- Data Mapping and Inventory: Maintaining a detailed inventory of all data collected, its source, purpose, location, and who has access to it. This is fundamental for compliance and enables quick responses to data subject requests.
- Consent Management Systems: Developing robust systems to manage and track user consent for data collection and processing, ensuring it aligns with legal requirements and user preferences.
A well-defined data governance framework acts as the backbone for ethical AI deployment, ensuring that data is handled responsibly from ingestion to insights. Without it, even the most advanced AI can become a privacy liability. Integrating ethical AI and strong data governance is crucial for effective Data Privacy Strategies in 2026.
Strategy 4: Global Regulatory Compliance and Consumer Rights
The global regulatory landscape for data privacy is complex and constantly evolving. From the GDPR in Europe to the CCPA in California and emerging regulations worldwide, businesses operate in an environment where non-compliance carries severe financial penalties and reputational damage. By 2026, a proactive and comprehensive approach to global regulatory compliance, coupled with a deep respect for consumer data rights, is an indispensable pillar of any effective set of Data Privacy Strategies.
Understanding and Adapting to Evolving Regulations
Businesses must move beyond a reactive stance and actively monitor and adapt to new and updated data protection laws:
- Dedicated Compliance Teams: Establishing or empowering dedicated teams responsible for staying abreast of regulatory changes across all relevant jurisdictions. This might involve legal, IT, and data privacy specialists.
- Cross-Border Data Transfer Mechanisms: Ensuring that mechanisms for transferring data across international borders (e.g., Standard Contractual Clauses, Binding Corporate Rules) are robust, up-to-date, and compliant with the latest legal interpretations (e.g., Schrems II implications).
- Regular Legal Audits: Conducting periodic legal reviews of data processing activities to ensure ongoing compliance with all applicable laws.
- Proactive Policy Updates: Developing agile internal policies and procedures that can be quickly updated to reflect new regulatory requirements, rather than waiting for enforcement actions.
The increasing convergence of data privacy laws, particularly around core principles like consent, data minimization, and individual rights, can simplify some aspects of compliance, but regional nuances remain critical. Companies operating globally must integrate these diverse requirements into a unified, yet adaptable, compliance framework.
Empowering Consumer Data Rights
Modern data privacy regulations heavily emphasize individual consumer rights over their personal data. Businesses must not only acknowledge these rights but also establish efficient and user-friendly mechanisms for consumers to exercise them:
- Right to Access: Providing consumers with easy ways to request and receive copies of their personal data held by the organization.
- Right to Rectification: Offering clear processes for consumers to correct inaccurate or incomplete personal data.
- Right to Erasure (Right to Be Forgotten): Implementing systems that allow consumers to request the deletion of their personal data under certain circumstances, and ensuring these requests are fulfilled promptly and thoroughly across all relevant systems.
- Right to Restriction of Processing: Enabling consumers to request the limitation of how their data is processed.
- Right to Data Portability: Allowing consumers to receive their personal data in a structured, commonly used, and machine-readable format, and to transmit that data to another controller without hindrance.
- Right to Object: Providing clear mechanisms for consumers to object to the processing of their personal data, especially for direct marketing purposes.
Many companies are now offering dedicated privacy dashboards or portals where users can manage their preferences, download their data, or submit deletion requests. This self-service approach not only improves efficiency but also significantly enhances the consumer experience and builds trust.
Vendor and Third-Party Compliance
The data privacy chain is only as strong as its weakest link. Businesses are often held responsible for the data privacy practices of their vendors and third-party partners:
- Due Diligence: Conducting thorough due diligence on all third-party vendors who will have access to or process personal data, ensuring they meet the same high standards of data protection.
- Contractual Obligations: Including stringent data protection clauses in all contracts with vendors, specifying responsibilities, security requirements, and breach notification protocols.
- Regular Audits of Vendors: Periodically auditing vendor compliance and security practices to ensure ongoing adherence to contractual agreements and regulatory requirements.
By extending their commitment to data privacy to their entire ecosystem of partners, businesses can mitigate risks and demonstrate a holistic approach to protecting consumer information. This comprehensive approach to global regulatory compliance and consumer rights is fundamental to robust Data Privacy Strategies in 2026 and beyond.
Conclusion: Building a Future of Trust Through Data Privacy Strategies
As we look towards 2026, the landscape of data privacy will continue to be defined by rapid technological advancements, evolving consumer expectations, and an ever-increasing web of regulatory requirements. For businesses, the choice is clear: either adapt and prioritize data privacy, or risk being left behind in a market where trust is the ultimate differentiator.
The four strategies outlined in this article — radical transparency and clear communication, robust cybersecurity and data protection, ethical AI and data governance, and comprehensive global regulatory compliance — are not isolated initiatives. Rather, they represent interconnected pillars of a holistic approach to data stewardship. When implemented together, these Data Privacy Strategies create a powerful framework that not only addresses current data privacy concerns but also builds a resilient foundation for future growth and innovation.
By embracing radical transparency, businesses empower consumers with knowledge and control over their data. By investing in robust cybersecurity, they safeguard that data from malicious actors. By committing to ethical AI and strong data governance, they ensure that data is used responsibly and fairly. And by navigating the complexities of global regulations and championing consumer rights, they demonstrate an unwavering commitment to legal and ethical data practices.
Ultimately, the goal is to transform data privacy from a perceived burden into a strategic asset. Organizations that proactively adopt these sophisticated Data Privacy Strategies will not only avoid penalties and reputational damage but will also cultivate deeper, more meaningful relationships with their customers. They will build a future where innovation and trust can coexist, where data can be harnessed for progress without compromising individual rights. In 2026 and beyond, consumer confidence will be directly proportional to a business’s demonstrated commitment to data privacy, making these strategies not just important, but absolutely essential for long-term success.